Every pull request should receive feedback
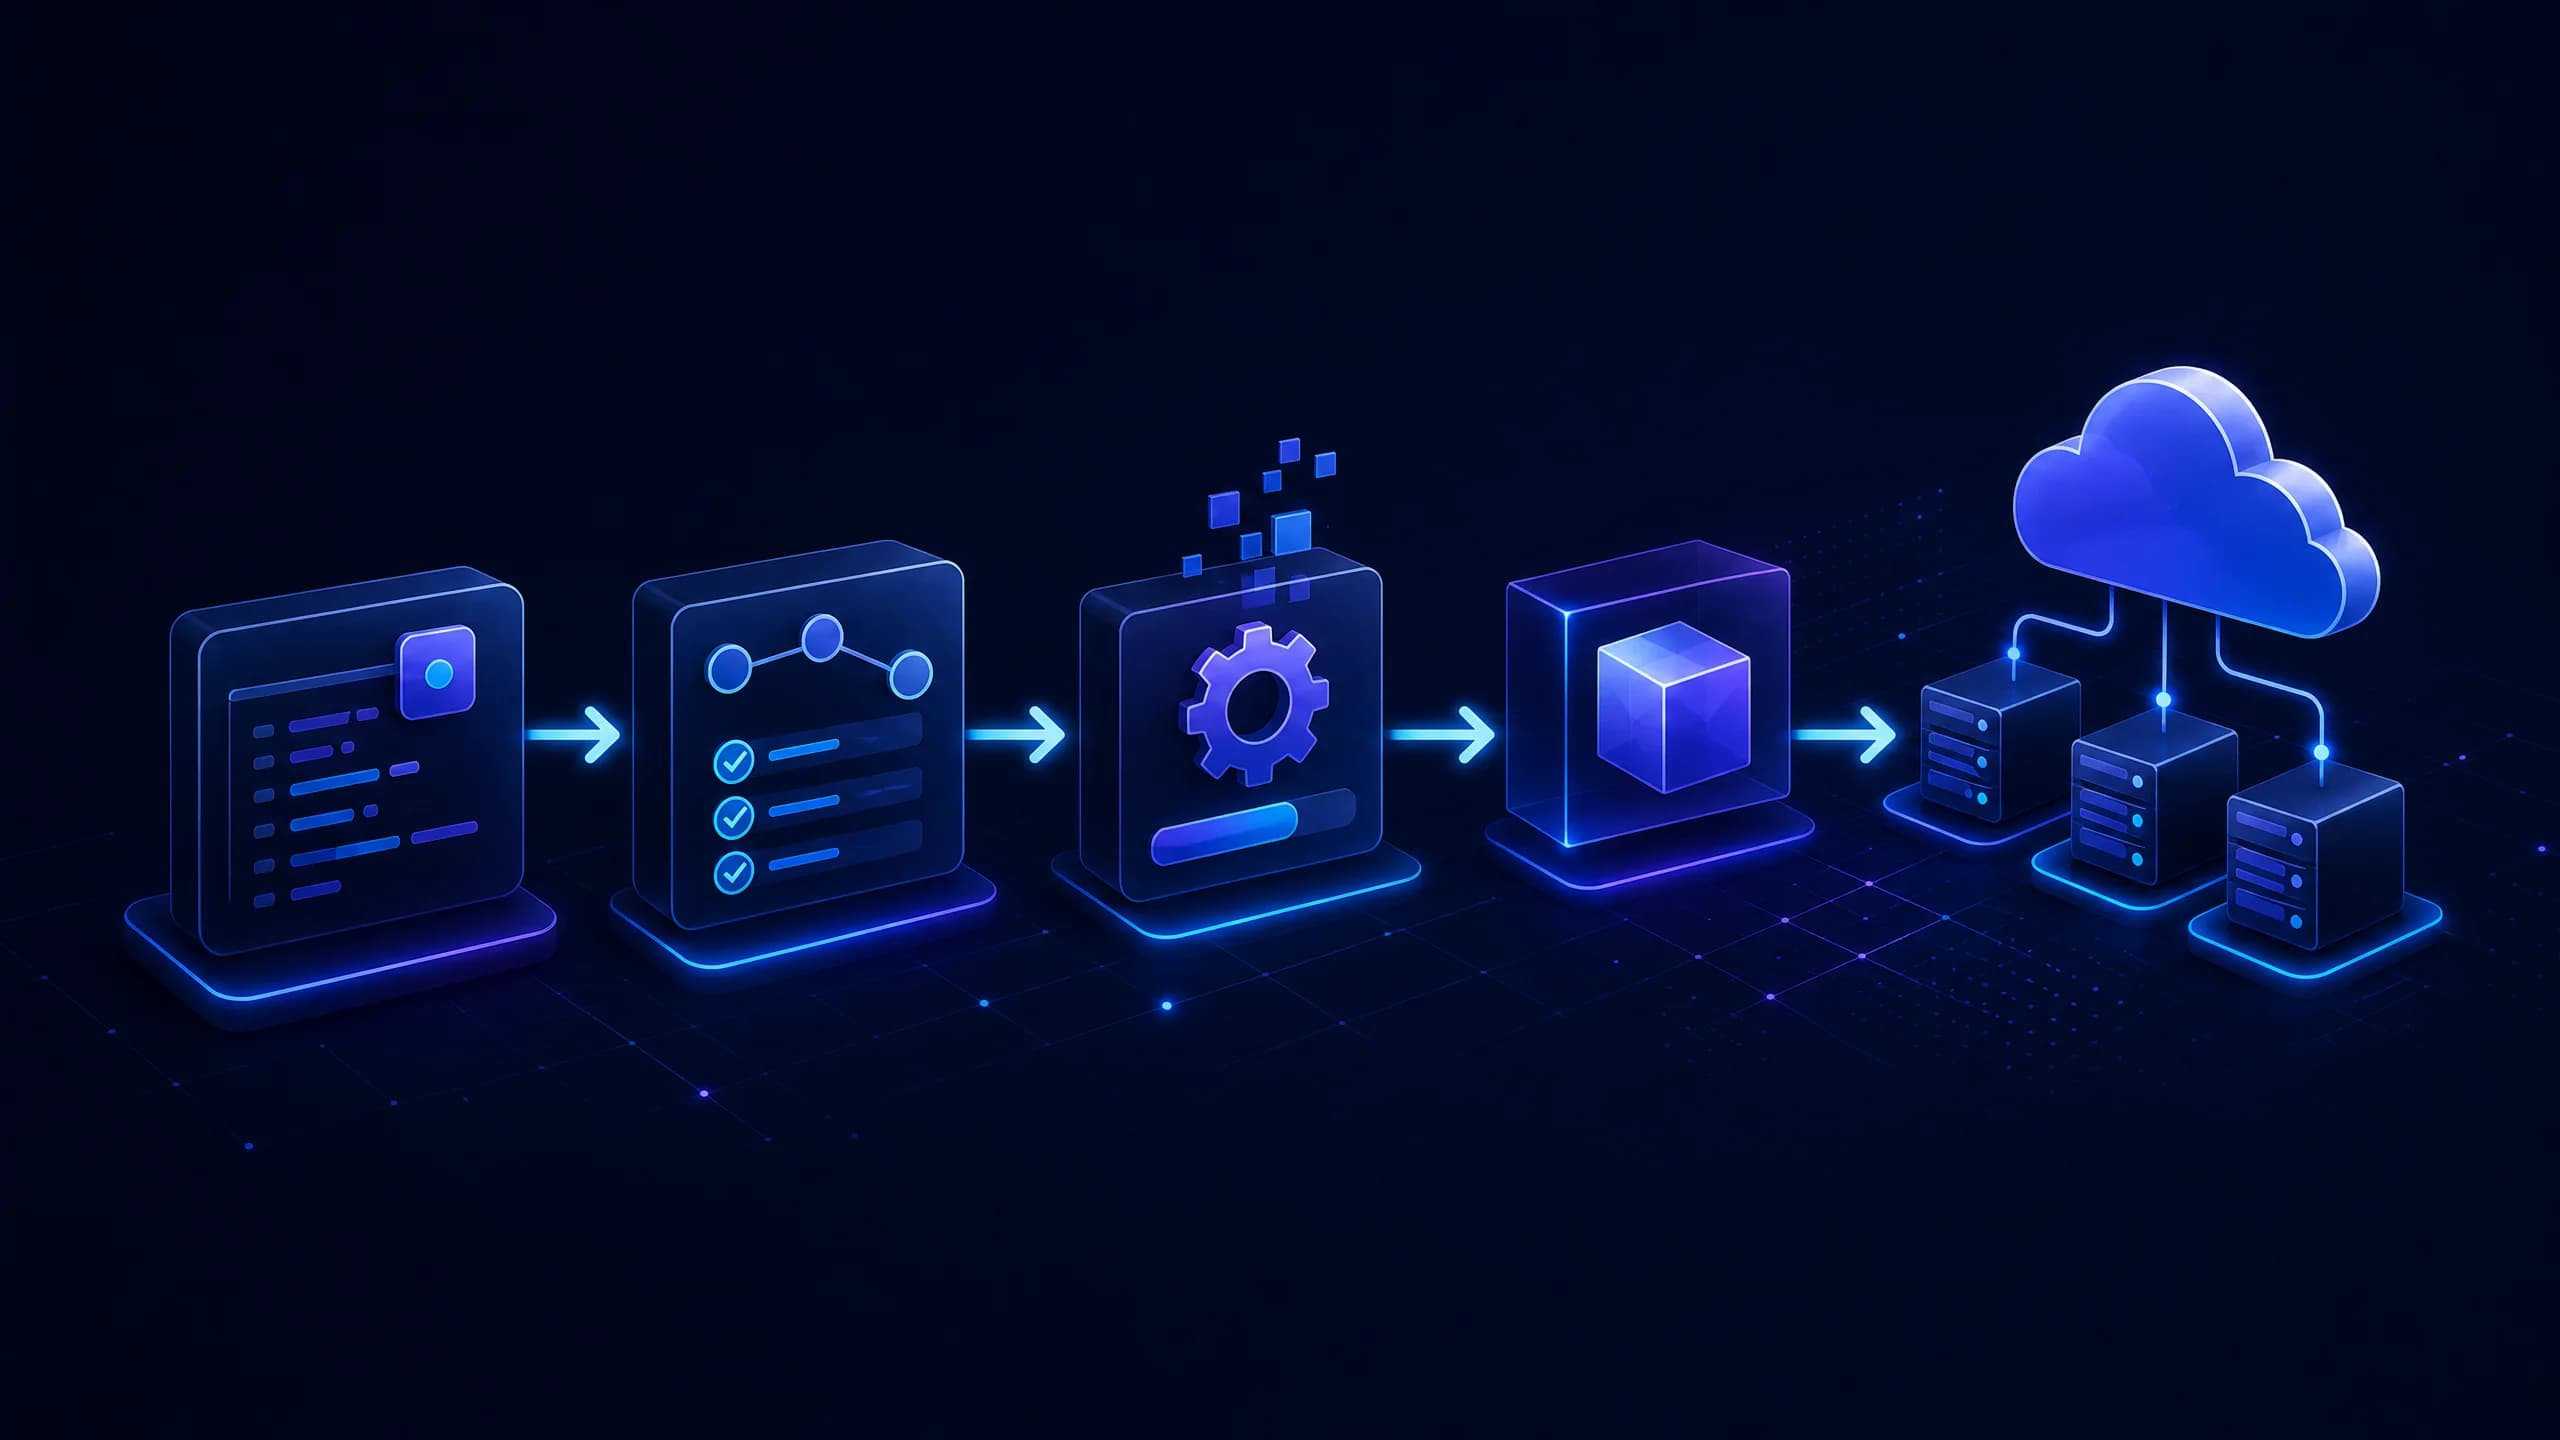
Start with a workflow that installs from the lockfile, runs type checking, executes tests, and performs linting. These checks should be fast enough that developers do not avoid them.
Separate verification from deployment
Build artifacts and deployment permissions should be protected. A common pattern is to verify every pull request, then deploy only from a trusted branch after the same checks pass.
Use caching carefully
Dependency caching can make workflows much faster, but the cache key should include the lockfile. A stale cache must never be allowed to hide a changed dependency graph.
Keep secrets out of logs
Use repository or environment secrets, give tokens the smallest required permissions, and avoid printing environment objects during debugging. CI is part of the application's security boundary.